Tor Browser 16.0: Firefox ESR 153, Redesigned Settings, and Generic Window Titles

Tor Browser 16.0: Firefox ESR 153, Redesigned Settings, and Generic Window Titles

The Tor Project has released Tor Browser 16.0, the first stable version built on Firefox ESR 153. This release is more than a routine update: it brings a completely redesigned settings interface, a new opt-in privacy feature called generic window titles, native ARM64 support for Linux, and a revamped offline manual.

For users who rely on Tor Browser for anonymity and censorship circumvention, version 16.0 represents a significant update that brings the browser in line with a year’s worth of Firefox changes while maintaining Tor’s privacy enhancements.

Continue reading →

Firefox: Upcoming Features: Bringing Tab Groups to Mobile and Privacy-First AI

Firefox: Upcoming Features: Bringing Tab Groups to Mobile and Privacy-First AI

Firefox is preparing a broad set of updates that will affect nearly every aspect of the browsing experience. The next wave of changes will focus on a cleaner interface, stronger privacy controls, smarter tab management, optional AI tools, and improved performance on both desktop and mobile devices. Rather than chasing trends for their own sake, the updates are centered on practical improvements that make the browser easier to use every day.

Continue reading →

Arista VeloCloud and Collabora/Nextcloud: Critical Flaws Actively Exploited

Arista VeloCloud and Collabora/Nextcloud: Critical Flaws Actively Exploited

Two critical vulnerabilities in widely used enterprise platforms are being exploited, and both have been added to the Known Exploited Vulnerabilities catalog of the Cybersecurity and Infrastructure Security Agency (CISA). Organizations running Arista VeloCloud Orchestrator on-premises or the Collabora Online Built-in CODE Server app for Nextcloud should treat this as an urgent incident response and patching priority.

Continue reading →

Spotify: Sharing a Family Plan Is Getting More Difficult With New QR Code Checks

Spotify: Sharing a Family Plan Is Getting More Difficult With New QR Code Checks

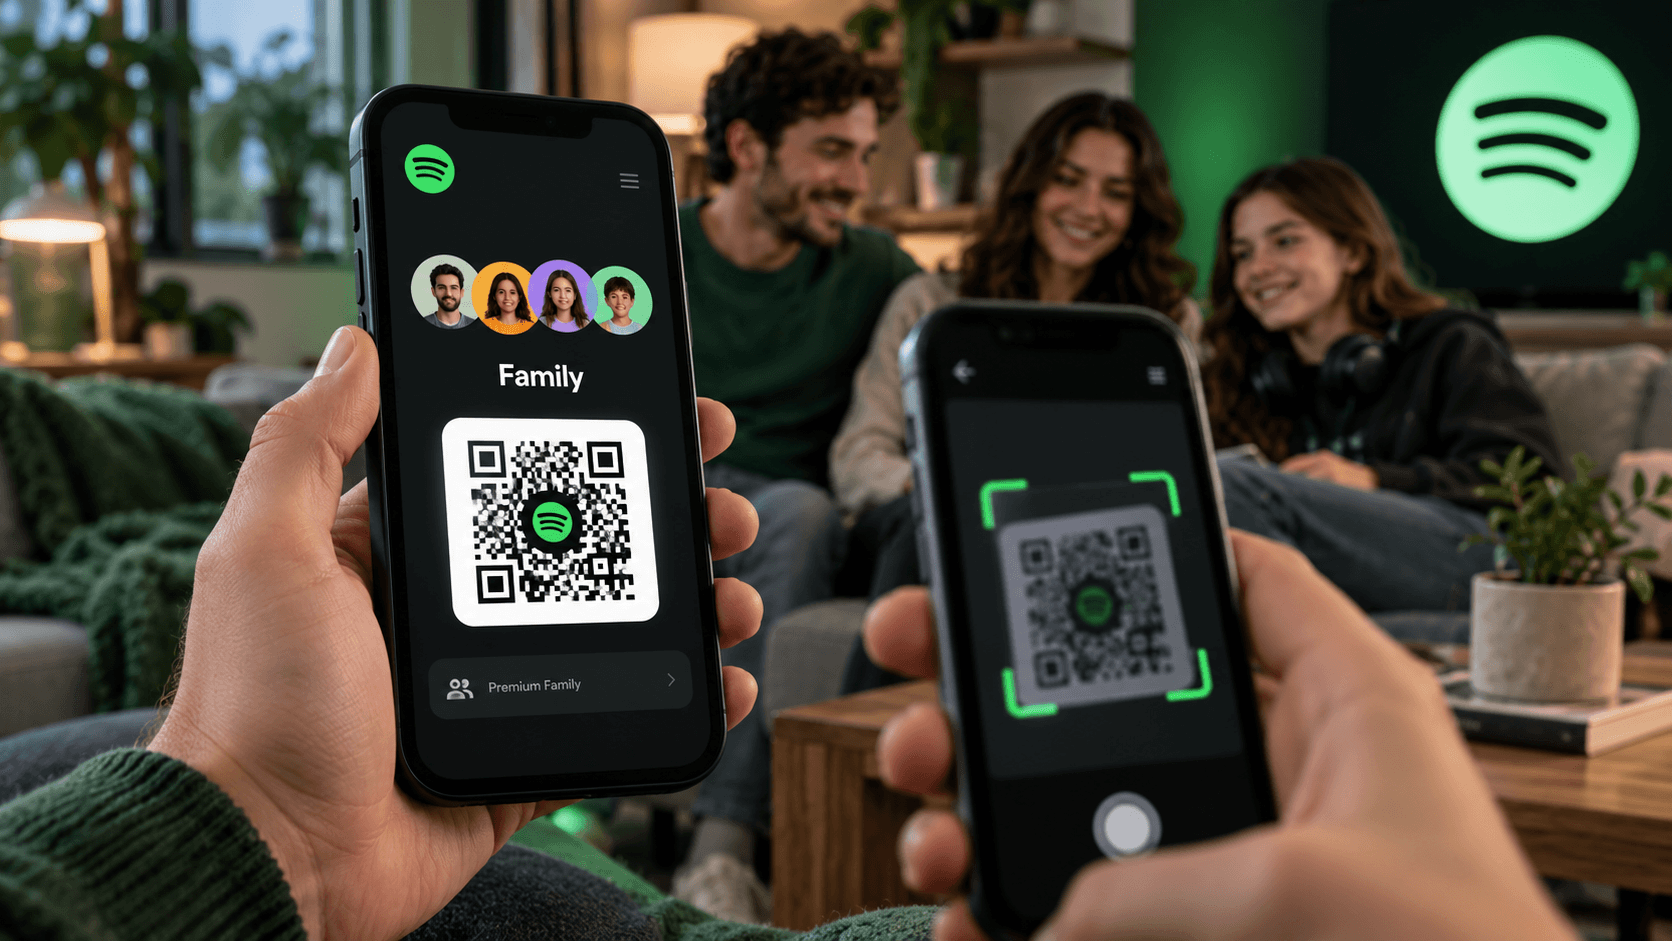
Spotify is tightening its rules for Premium Family subscriptions. The music streaming service has introduced a new QR code verification system to ensure that all subscribers to a Premium Family plan live at the same address.

Previously, members only needed to provide the same residential address as the subscription owner. However, Spotify may now require them to scan a QR code in person to prove that they live in the same household as the subscription owner. Users who fail to complete the verification process within seven days may face significant restrictions.

Continue reading →

PHP: Critical Security Vulnerabilities Allow Remote Code Execution – Updates Released for All Supported Versions

PHP: Critical Security Vulnerabilities Allow Remote Code Execution - Updates Released for All Supported Versions

On 21 October 2026, the PHP development team released emergency security updates to address two critical vulnerabilities that could allow attackers to execute malicious code on vulnerable web servers without authentication.

The vulnerabilities, tracked as CVE-2026-109618 and CVE-2026-109619, have each received a CVSS 4.0 severity score of 9.2 out of 10. Collectively known as PHP2Shell, they affect the PHP runtime itself rather than individual applications.

These vulnerabilities are particularly dangerous because PHP is used by many content management systems, including WordPress, Joomla and Drupal, as well as countless other websites and web applications.

Continue reading →

OpenAI: ChatGPT Chats Can Now Be Protected With a PIN

OpenAI: ChatGPT Chats Can Now Be Protected With a PIN

OpenAI has introduced a new privacy feature for ChatGPT that allows users to protect individual conversations with a four-digit PIN. The feature, called Locked Chats, is designed to prevent others from accessing sensitive conversations when using a shared device or viewing someone’s ChatGPT account.

Locked Chats was announced on 20 October 2026 and is gradually being rolled out to users with all major ChatGPT subscription plans, including the free version.

Continue reading →

Electronic Arts: EA Advertising Turns Games Into an Advertising Platform

EA Advertising

Electronic Arts is significantly expanding its advertising business. With EA Advertising, the publisher is launching its own platform designed to integrate brands more deeply into EA games in the future.

This isn’t just about traditional on-screen advertising. Rather, EA aims to integrate brands directly into digital game worlds-for example, through stadium billboards, jerseys, challenges, rewards, broadcast overlays, or even its own playable content.

Continue reading →

Netflix Cheaper: For $3.75/Month with VPN (Turkey, India) – Easy Guide

Netflix cheaper via VPN

Netflix is one of my favourite streaming services, but the monthly cost can really add up. I discovered that Netflix charges different prices in different countries. By using a VPN to sign up from countries like Turkey or India, I managed to pay much less for the same service. With a bit of effort, I turned my premium Netflix subscription into a much more affordable deal by subscribing through Turkey and India using a VPN.

In this post, I’ll share my own test results and a step-by-step guide so you can try it too. This includes how to use a VPN for Netflix, setting up an account in Turkey (with gift cards) or India (with credit card), important tips, and everything else I learned along the way. The tone is slightly personal because I’ve actually tested these methods myself, and I want to help you save money on Netflix in a factual, straightforward way.

Continue reading →

WordPress: Security Vulnerability Discovered in Plugins

Wordpress Security

The security firm Wordfence has made a troubling discovery: identical malicious code has been found in five different plugins for the popular content management system WordPress. This poses a serious threat to the security of numerous websites.

The discovered malicious code has far-reaching consequences. It allows attackers to steal database credentials and create unauthorized administrator accounts. Additionally, malicious JavaScript code can be injected into the footer of web pages to spread SEO spam.

Particularly concerning is the fact that only one of the affected plugins, “Social Warfare,” has a security update available. For the other infected plugins – “Blaze Widget,” “Wrapper Link Elementor,” “Contact Form 7 Multi-Step Addon,” and “Simply Show Hooks” – there are currently no clean versions available.

As an immediate measure, WordPress has suspended the download of the affected plugins. Website operators who have installed any of these plugins should consider their site compromised and promptly take security measures. These include reviewing and cleaning up administrator accounts and thoroughly examining the entire installation for further malicious code infections.

This discovery once again underscores the importance of regular security updates and vigilant monitoring of WordPress installations. Given the multitude of available plugins and the frequency of security vulnerabilities, it is essential for website operators to stay up-to-date with security developments.